Integration Consumers
An Integration Consumer represents a system that connects to the Jomablue APIs, for example your CRM, registration platform, or an exhibitor database. Each Consumer holds its own access scope and its own tokens, so you can connect several systems independently and grant each one only the access it needs. This article walks through creating a Consumer, configuring its scope and token validity, and generating a long-lived token.
A single Consumer can be granted access across the Ingest API, the Updates API, and the Event Discovery API. You can create as many Consumers as you need.
Before you start
You need:
- Portal access with the trusted-admin-integrator or owner role.
- If you plan to scope the Consumer to specific endpoints rather than all of them, any endpoints you want to grant already created.
Step 1: Open the Integration Consumers tab
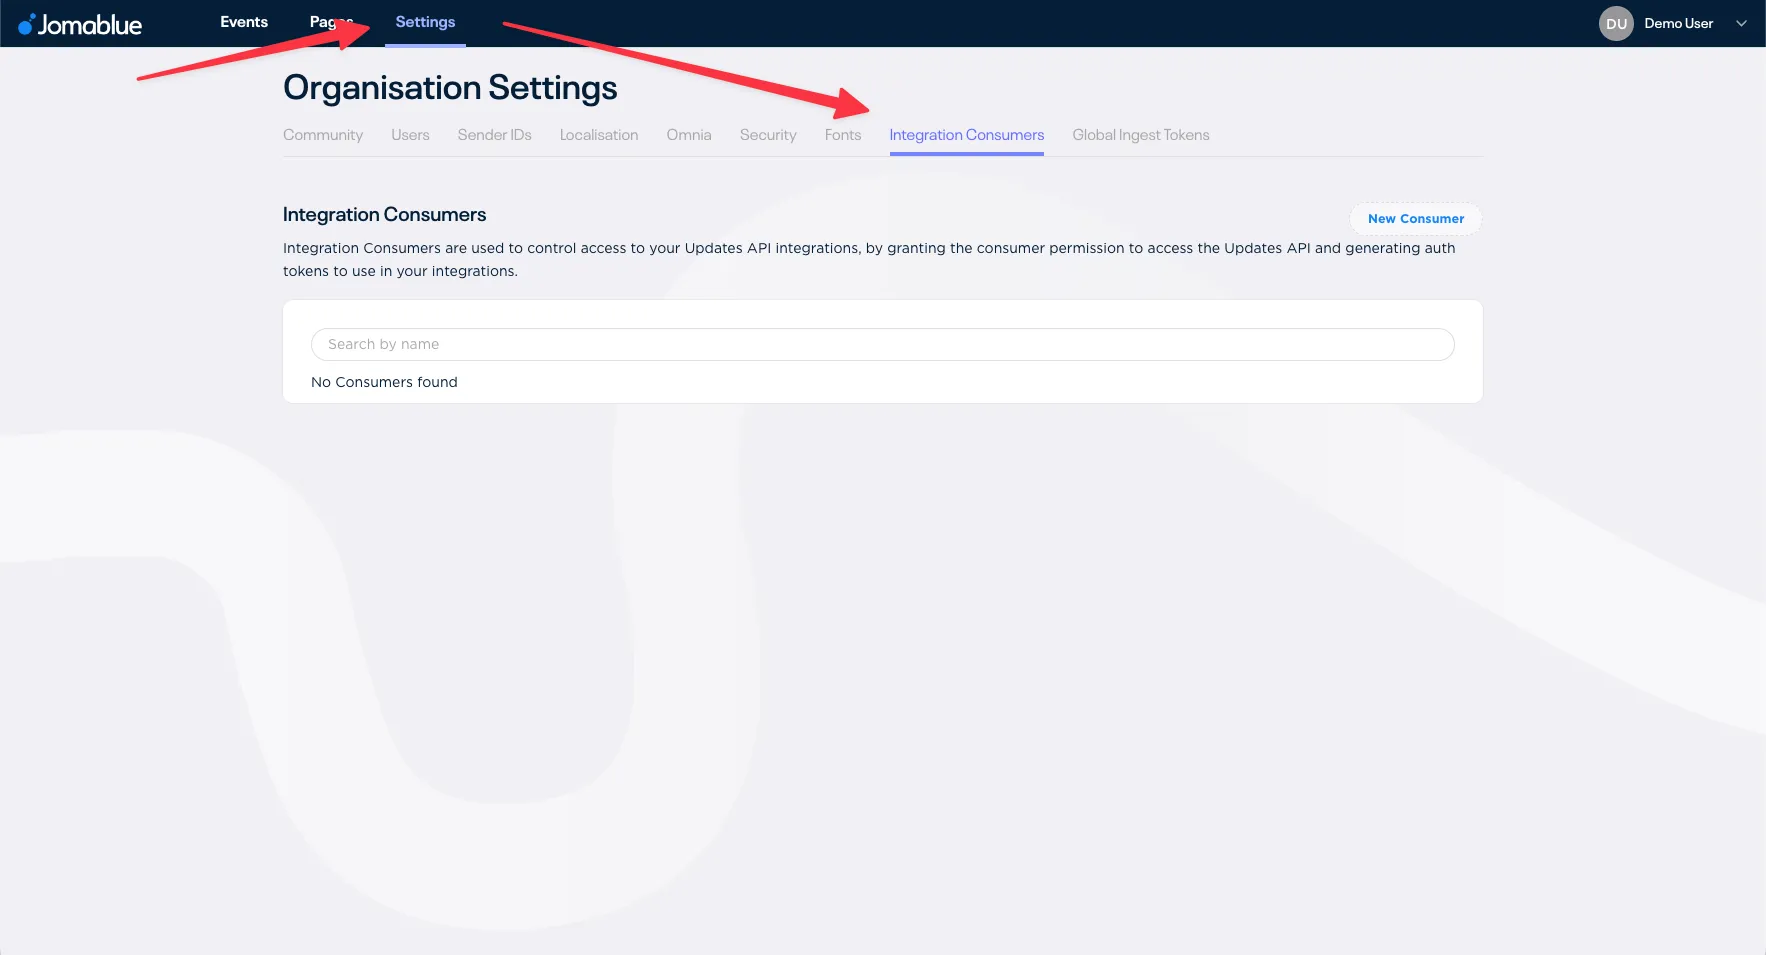
Open the Settings tab at the top of the page, then click the Integration Consumers tab.
Step 2: Add the Consumer
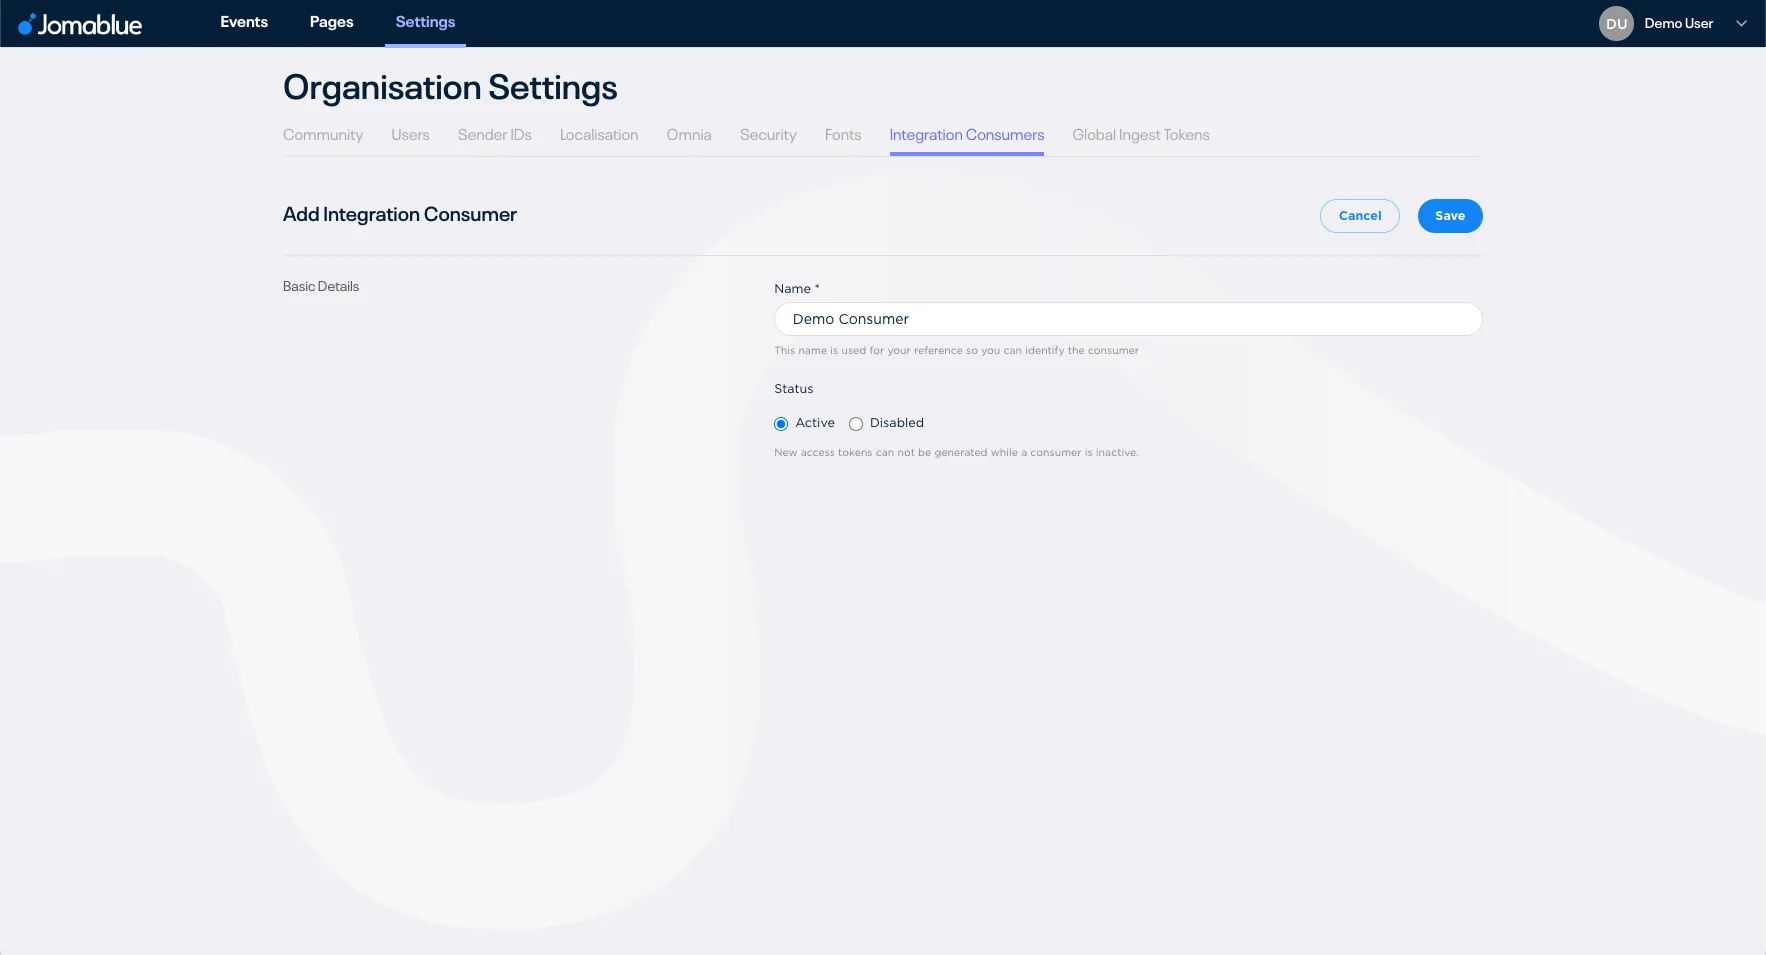
Click New Consumer, give the Consumer a name, and click Save. The name is for your own reference, so use something that identifies the connecting system, for example "CRM sync" or "Registration platform".
Leave the Consumer active so its tokens can authenticate. Setting a Consumer to inactive stops all of its tokens from authenticating without deleting them.
Step 3: Configure access
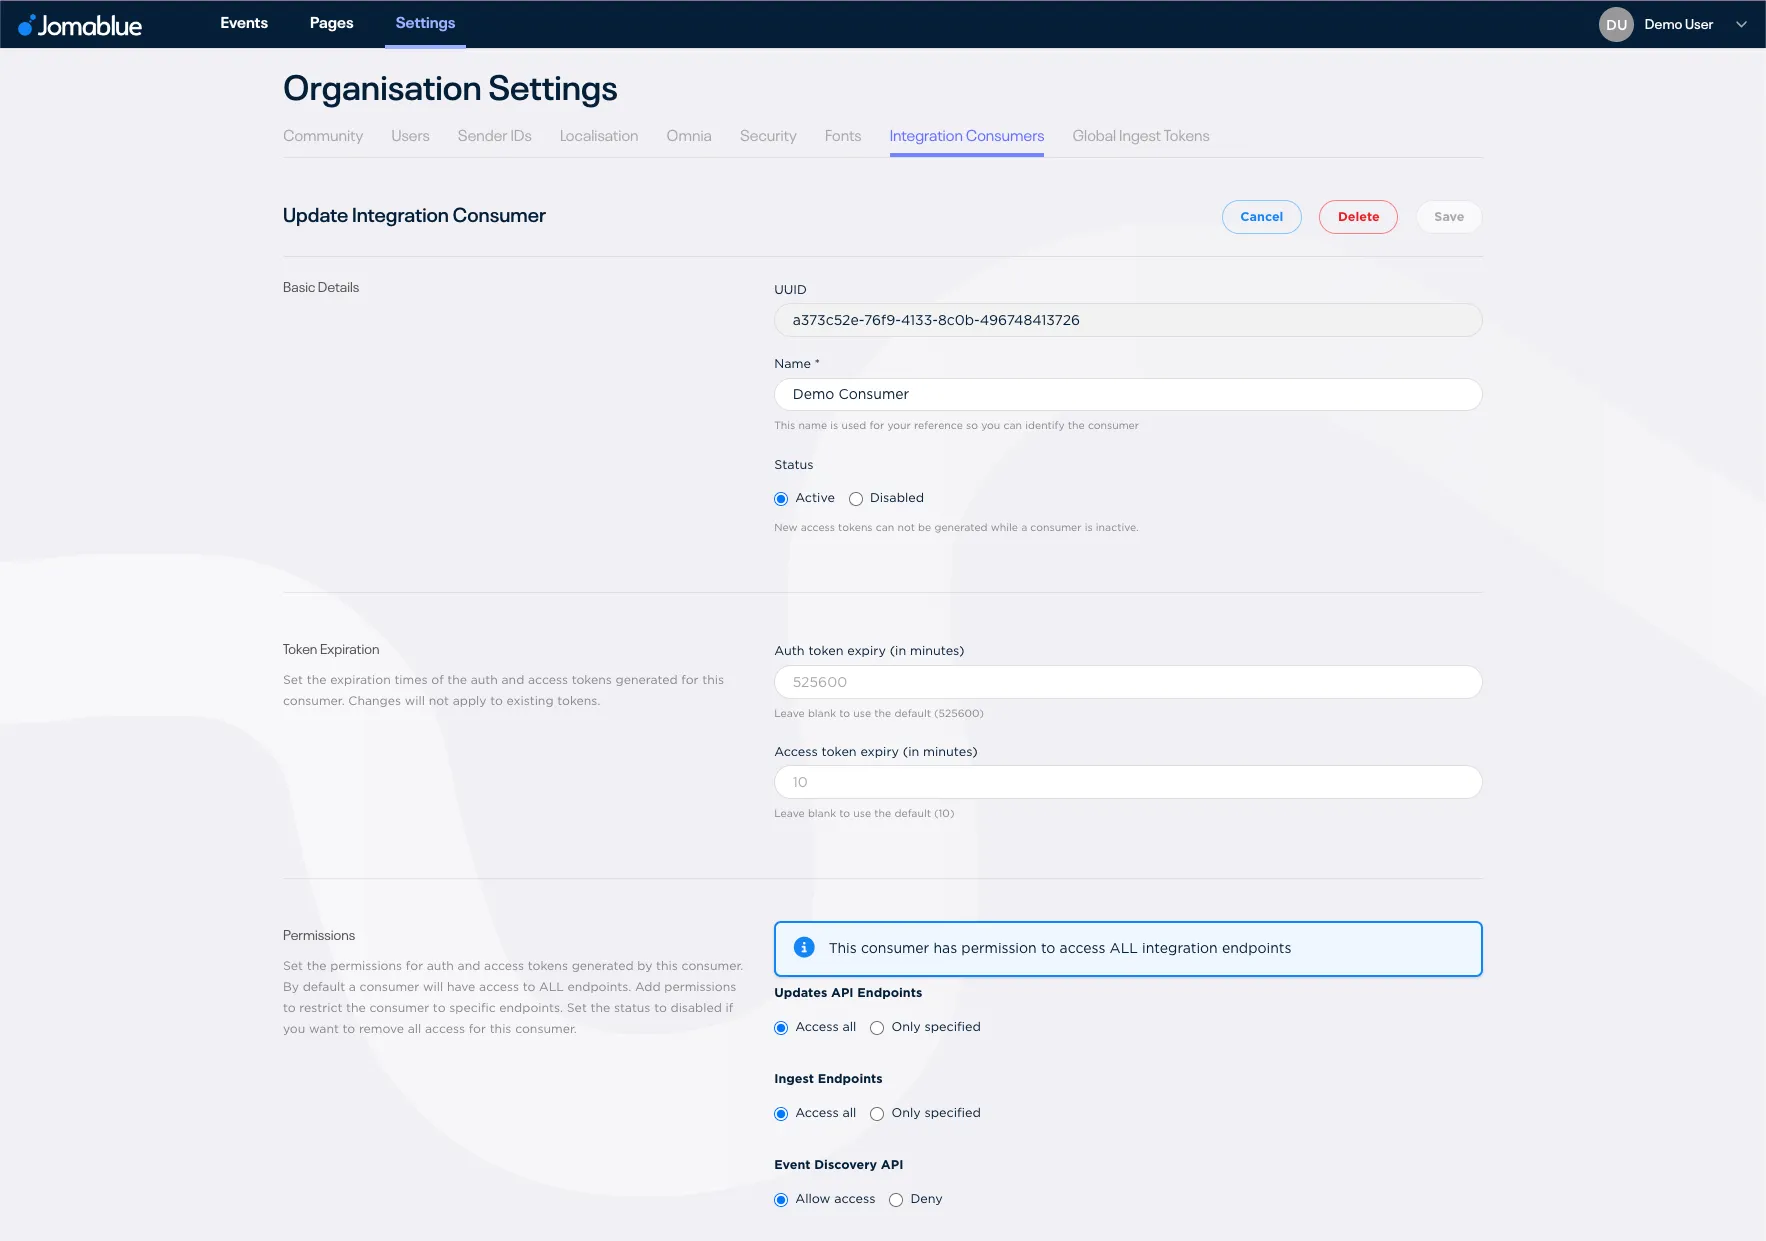
Locate the Consumer you just created and click Edit. All three APIs are granted by default, so narrow the scope to only what the connecting system needs:
- Ingest API: grant all Ingest endpoints, or select specific endpoints.
- Updates API: grant all Updates endpoints, or select specific endpoints.
- Event Discovery API: grant on or off.
Grant only what the connecting system needs. For example, a registration platform that only sends data in might be granted a single Ingest endpoint, while a CRM that reads data back is granted specific Updates endpoints.
Step 4: Set token validity (optional)
The Consumer issues two kinds of token: a long-lived token used to request access tokens, and the short-lived access tokens sent on API requests. You can set a custom validity period for each to suit your security requirements, or leave them at their defaults. Each has a maximum it cannot exceed.
Click Save when the Consumer is configured.
Step 5: Generate a long-lived token
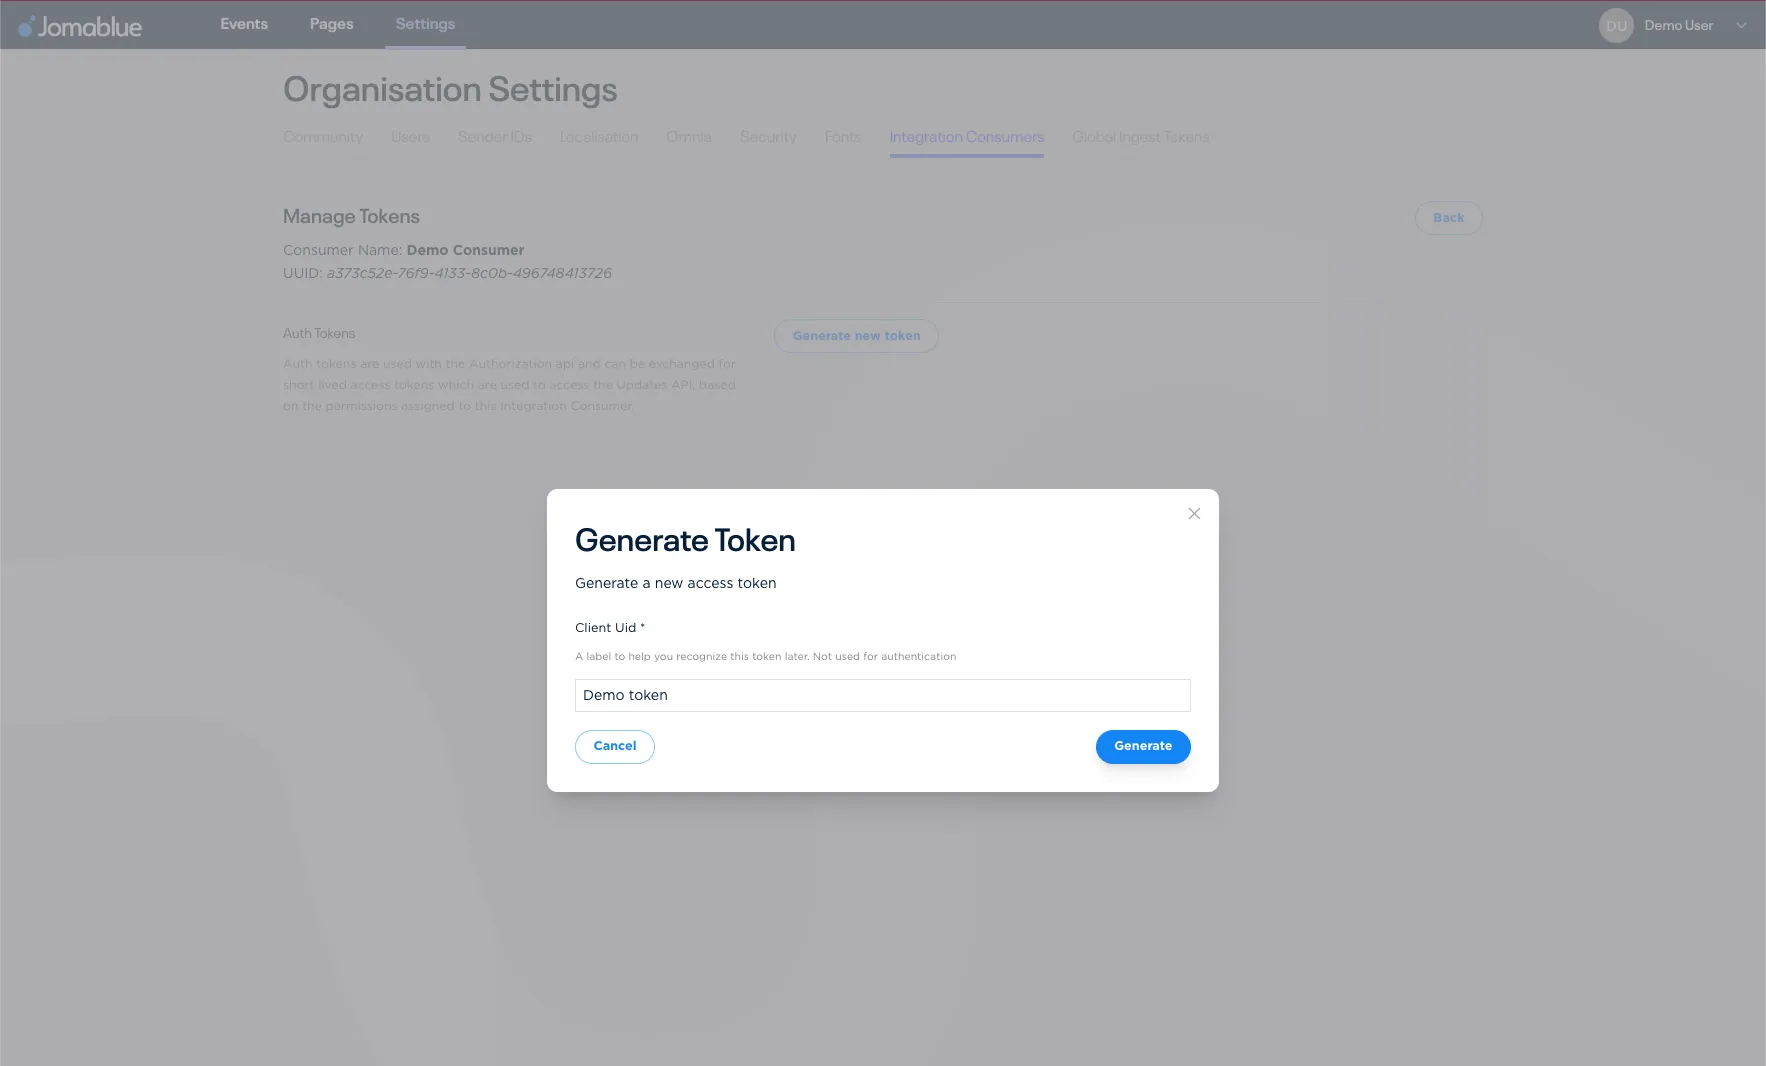
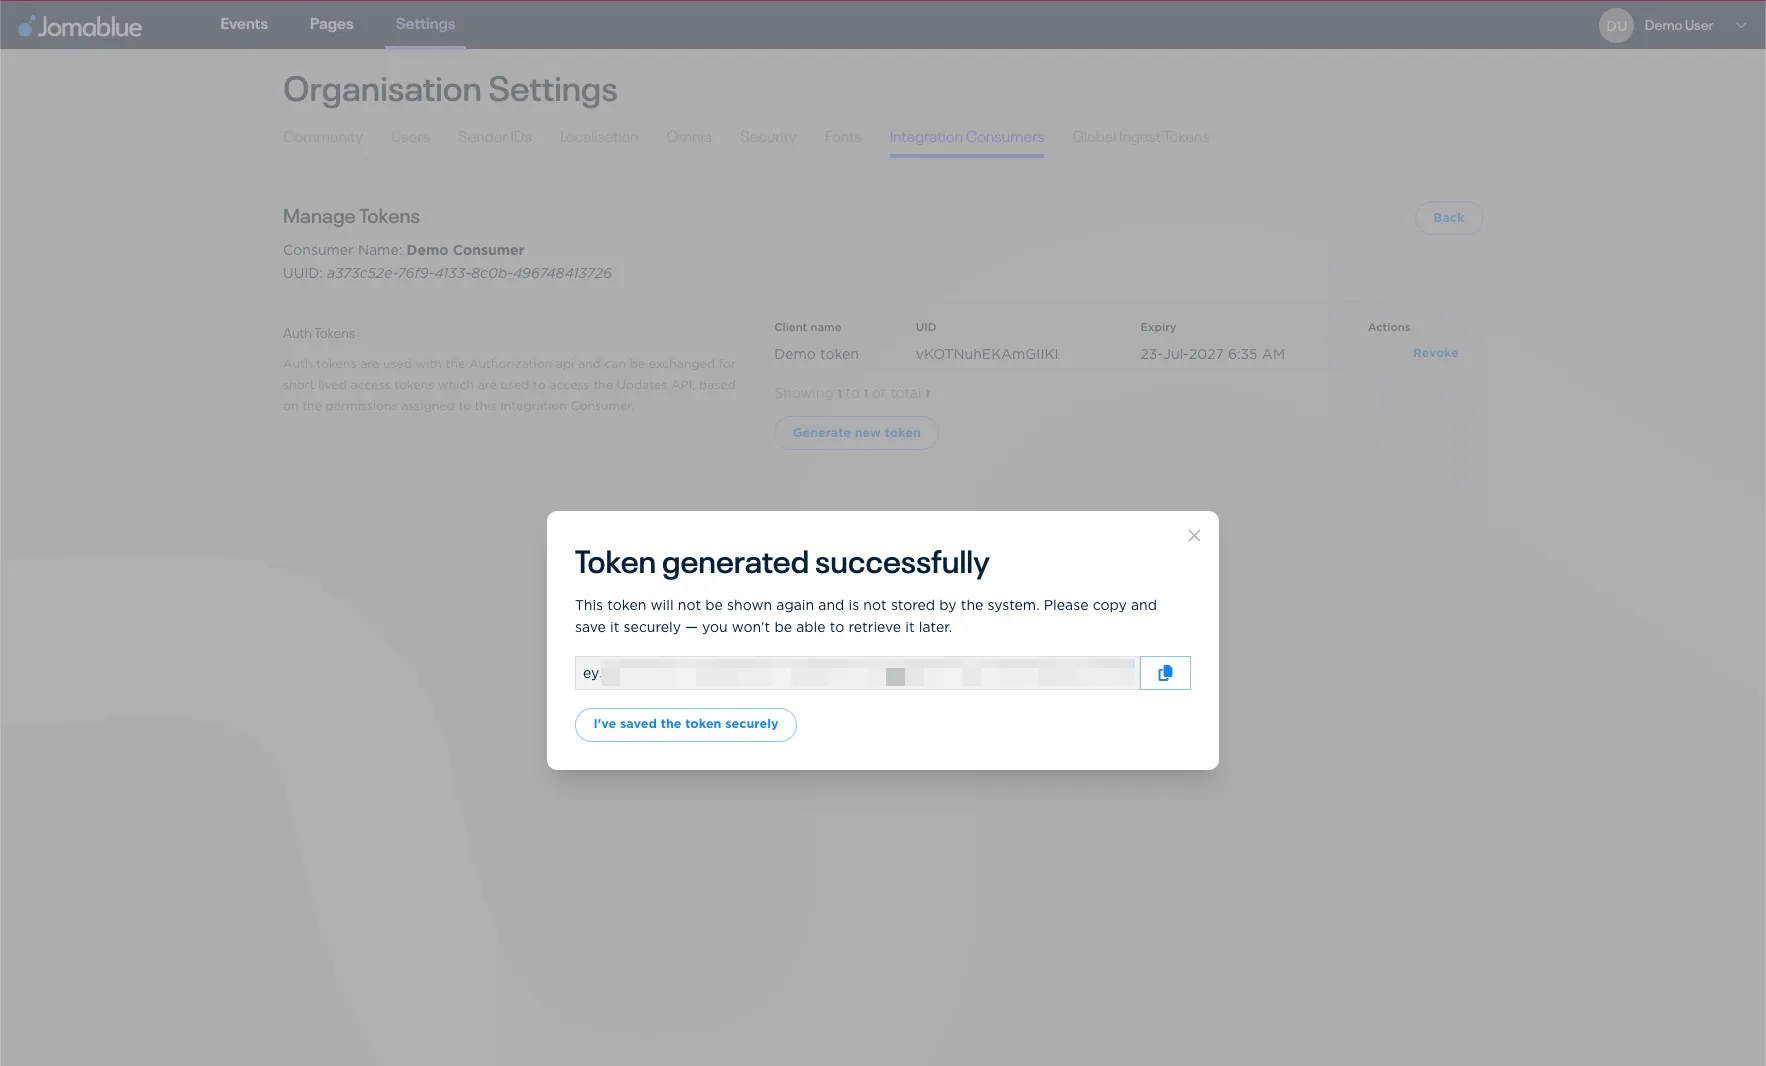
Locate the Consumer in the list and click Manage Tokens, then click Generate new token. Give the token a client identifier that labels where it will be used, so you can tell your Consumer's tokens apart later.
Step 6: Copy the token
The token is displayed only once, so copy the value and store it securely before leaving the screen. If you lose it, generate a new token rather than trying to recover the old one. Treat it like a password: it grants access to the Consumer's scope, so keep it out of source control and shared logs.
This is the long-lived token you exchange for a short-lived access token when calling the API. See Authentication for the token exchange, or the Ingest API Authentication article if you are posting payloads in.
Managing tokens
A Consumer can hold more than one long-lived token at a time. Each token is listed with its client identifier and expiry, so you can see what is in use.
To rotate a token, generate a new one, move your systems over to it, then revoke the old one. Revoking a token stops it authenticating immediately, so rotate before the old token expires to avoid an interruption.
Verify
Confirm the Consumer works end to end by exchanging its long-lived token for a short-lived access token:
A successful response returns a short-lived access token in the data field. Send that token as the Bearer token on your API requests. For the full flow, see Authentication.